One team instead of a tool, a consultant and an auditor chase
Many teams buy a compliance platform, then pay a consultant or vCISO to do the work in it, then manage auditors and pen testers separately. Keldyn puts the platform and qualified auditors and security specialists in one team, and builds compliance into how your engineers ship.
What you're actually paying for
| Cost line | Usual setup | With Keldyn |
|---|---|---|
| Compliance platform | A separate tool your team or consultant has to keep up to date. | The Keldyn platform, built into your engineering workflow. |
| Consultant / virtual CISO doing the work | An outside adviser, engaged separately, working inside the tool. | A customer success team of qualified auditors and security specialists. |
| Auditor | Found, contracted and managed by you. | We prepare you and introduce independent auditors. |
| Pen test | Sourced and scheduled separately. | We can introduce a pen-test partner. |
Who does the work
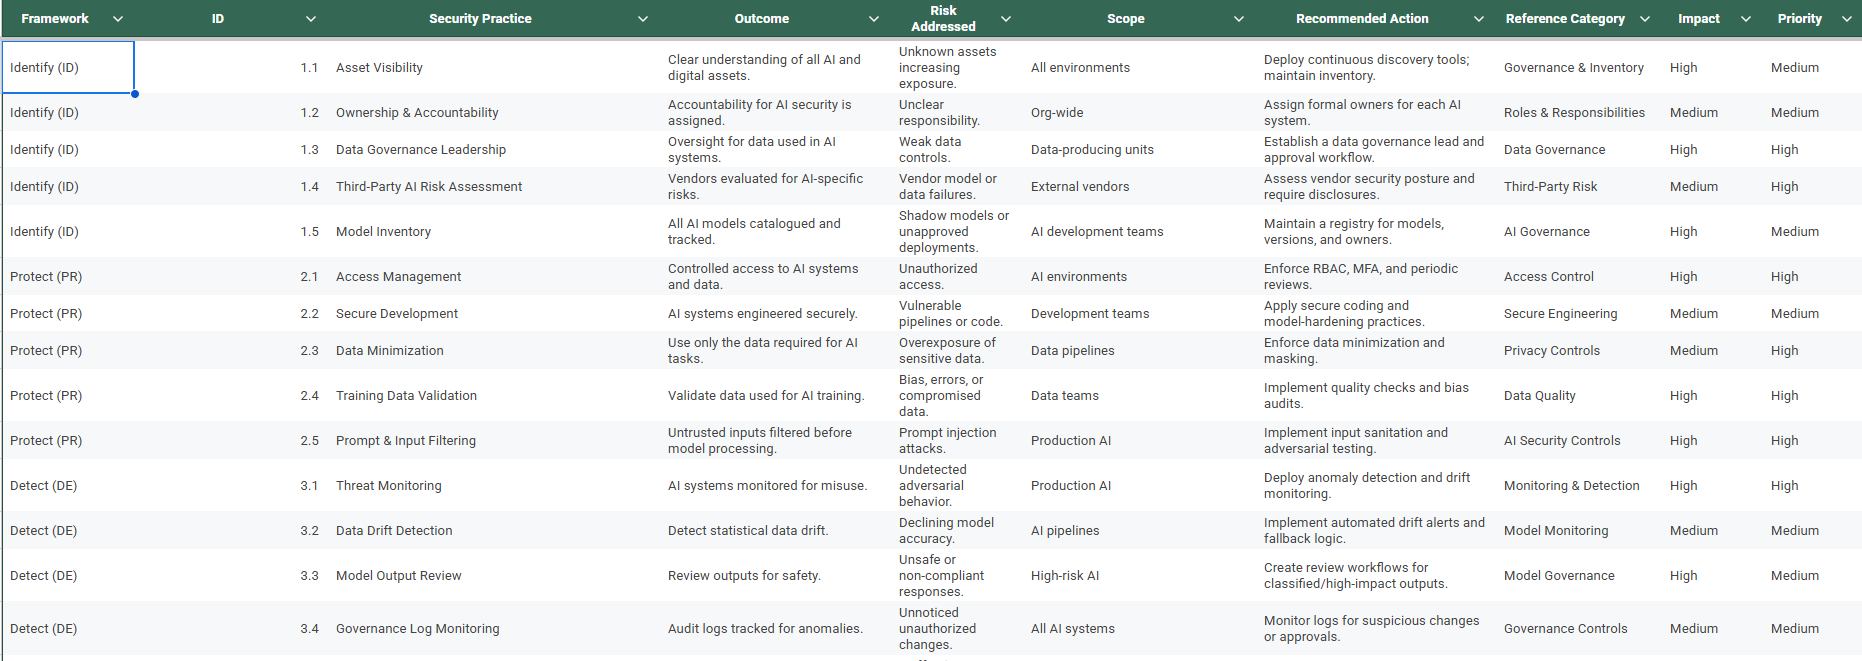
The usual setup
Screenshots and evidence chasing after the fact, once the work is already done.
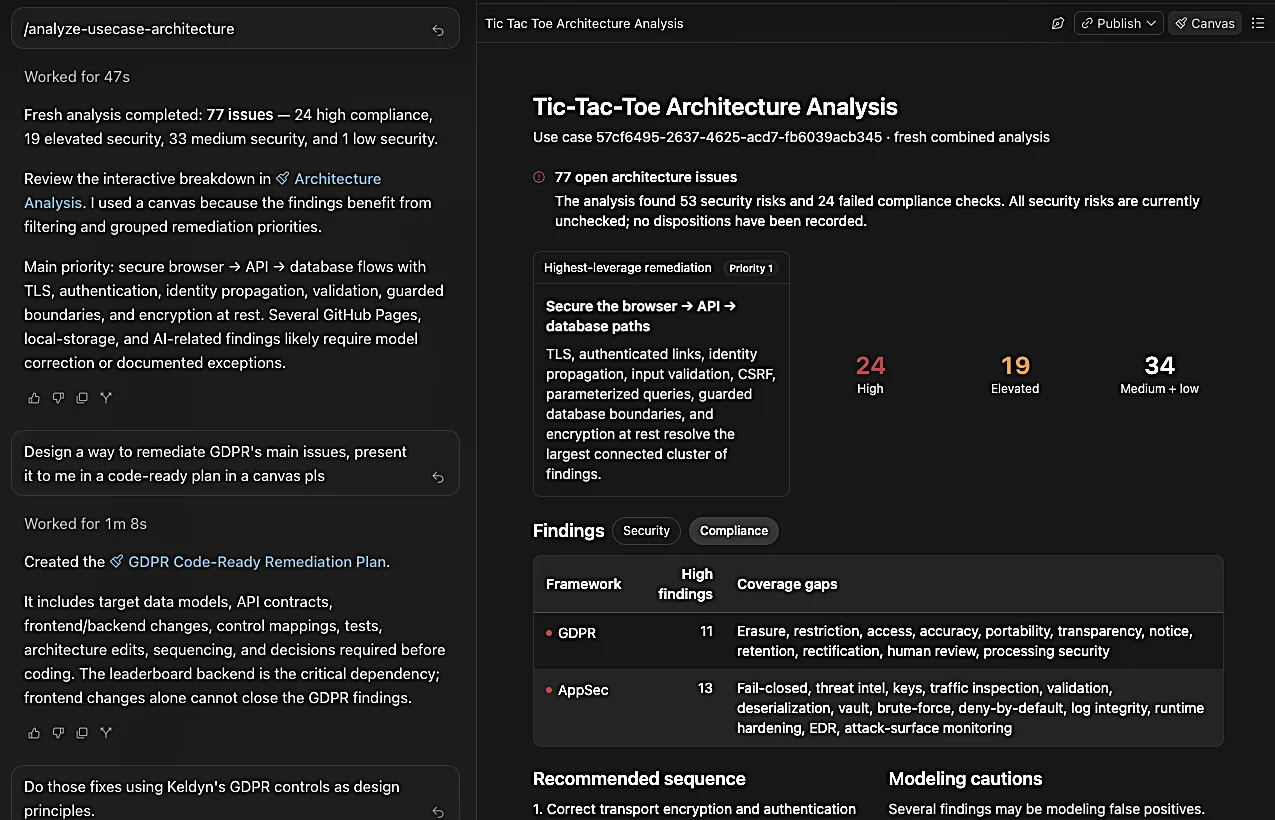
With Keldyn
Your coding agents get your requirements before they build. Every change is checked against your rules before merge. Evidence is collected as you ship.
Audit you can trust
Independent auditors
Independent auditors issue the report or certificate, not us.
Traceable evidence
Evidence is traceable to the actual code change.
We hold it too
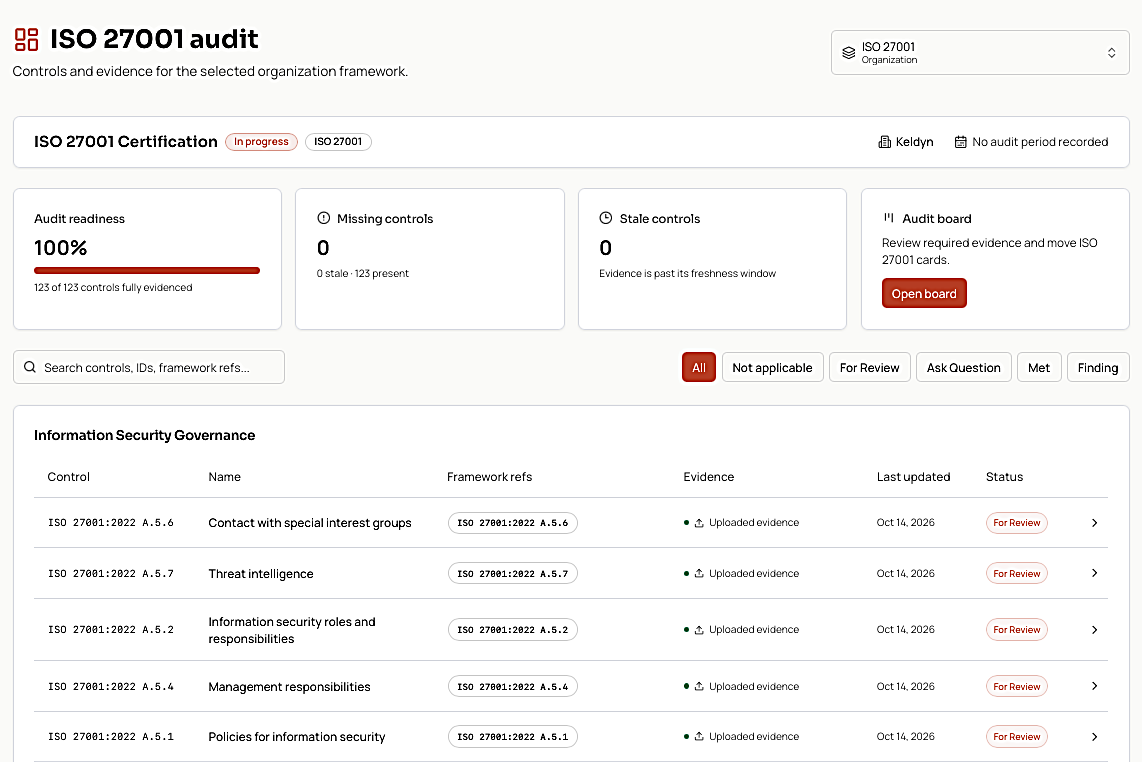
Keldyn itself holds ISO 27001.
SOC 2 reports come from an independent CPA. ISO certificates come from an accredited body. We introduce you, and we're in the room.
ISO 27001 certified
"Everyone I know who has been through SOC 2 after the fact describes the same thing. Months of hunting down evidence for decisions nobody wrote down at the time."
 Tim Brown, Co-Founder, Kyance
Trust infrastructure for agentic commerce
Mapped while the architecture was still moving.
Findings surface in the coding agent and land in Jira.
Fixes and configuration build up against the audit from the start.
Questions
Can we keep our current tool?
Yes. Keldyn can sit in your engineering workflow first, and you can move your compliance programme across when you are ready.
Do you do the audit?
No. An independent auditor issues the report or certificate. We prepare you and introduce you to them.
Do you do pen testing?
We introduce you to a pen-test partner.