ISO 27001 certification: a guide for software and AI companies
ISO/IEC 27001:2022 sets requirements for an information security management system (ISMS). ISO 27001 certification shows that your ISMS meets the standard, within the scope assessed by the certification body.
- Standard
- ISO/IEC 27001:2022. The transition period from the 2013 version has ended.
- What it is
- Requirements for an information security management system (ISMS).
- What's involved
- Scope, risk assessment, Annex A controls and a Statement of Applicability.
- Who checks it
- An accredited certification body, in Stage 1 and Stage 2 audits.
- Cycle
- Three years, with surveillance audits before recertification.
On this page
Use ISO/IEC 27001:2022
The transition period from ISO/IEC 27001:2013 has ended. Prepare against ISO/IEC 27001:2022, with a clear scope covering the people, systems, services and information you need to protect.
The ISO 27001 certification cycle
- Preparation
Scope, risk assessment, controls
- Stage 1 audit
Documentation and readiness
- Stage 2 audit
Implementation and effectiveness
- Certificate
- Surveillance audit
- Surveillance audit
- Recertification
Risk assessment and Annex A controls
Identify and assess information security risks, decide how to treat them and document your decisions. Annex A provides reference controls across organisational, people, physical and technological themes.
Your Statement of Applicability records the controls you need, why they apply, whether they are implemented and the justification for exclusions. Do not treat Annex A as a checklist to apply without considering your risks.
Stage 1 and Stage 2 certification audits
An accredited certification body carries out the certification audit. Stage 1 reviews your scope, management-system documentation and readiness for Stage 2.
Stage 2 assesses implementation and effectiveness, including evidence that the controls and management processes operate in practice. Address findings through the certification body’s process.
Surveillance audits and the three-year cycle
Certification follows a three-year cycle with surveillance audits between the initial certification and recertification. Keep risk assessments, internal audits, management reviews and corrective actions active between external audits.
Engineering work as evidence
- Architecture documentation and decisions show how security requirements informed the design.
- Pull request reviews and recorded checks help demonstrate change control and secure development practices.
- Access reviews, dependency decisions and incident records support the controls they relate to.
Evidence needs context: which control it supports, who reviewed it and what action followed. Evidence from checks helps an auditor assess the control; it does not replace the audit.
Adding AI governance
Teams using or developing AI can add an AI management system alongside their ISMS. ISO 42001 has AI-specific requirements; ISO 27001 certification alone does not establish that system.
SOC 2, ISO 27001 and ISO 42001 compared
| Topic | SOC 2 | ISO 27001 | ISO 42001 |
|---|---|---|---|
| What it is | Attestation report | Certification of an information security management system | Certification of an AI management system |
| Who issues it | Independent CPA firm | Accredited certification body | Accredited certification body |
| What it covers | Controls against the Trust Services Criteria in your scope | Your ISMS and Annex A controls, within the certified scope | Your AI management system, including AI risk, impact assessment and the AI system life cycle |
| Validity | The report covers a period; buyers usually expect a recent report | 3-year certificate with annual surveillance audits | 3-year certificate with annual surveillance audits |
| Common buyers | US-led buyers often ask for SOC 2 | UK and EU buyers often ask for ISO 27001 | Buyers with AI-specific governance questions |
How Keldyn helps
Check the design
Your coding agent maps your architecture. Keldyn builds a threat model and checks it against your frameworks before the build.
Security by design and threat modelling →Review changes
Check AI-written code against your security and compliance requirements before it merges.
AI code review and secure coding →Prepare your evidence
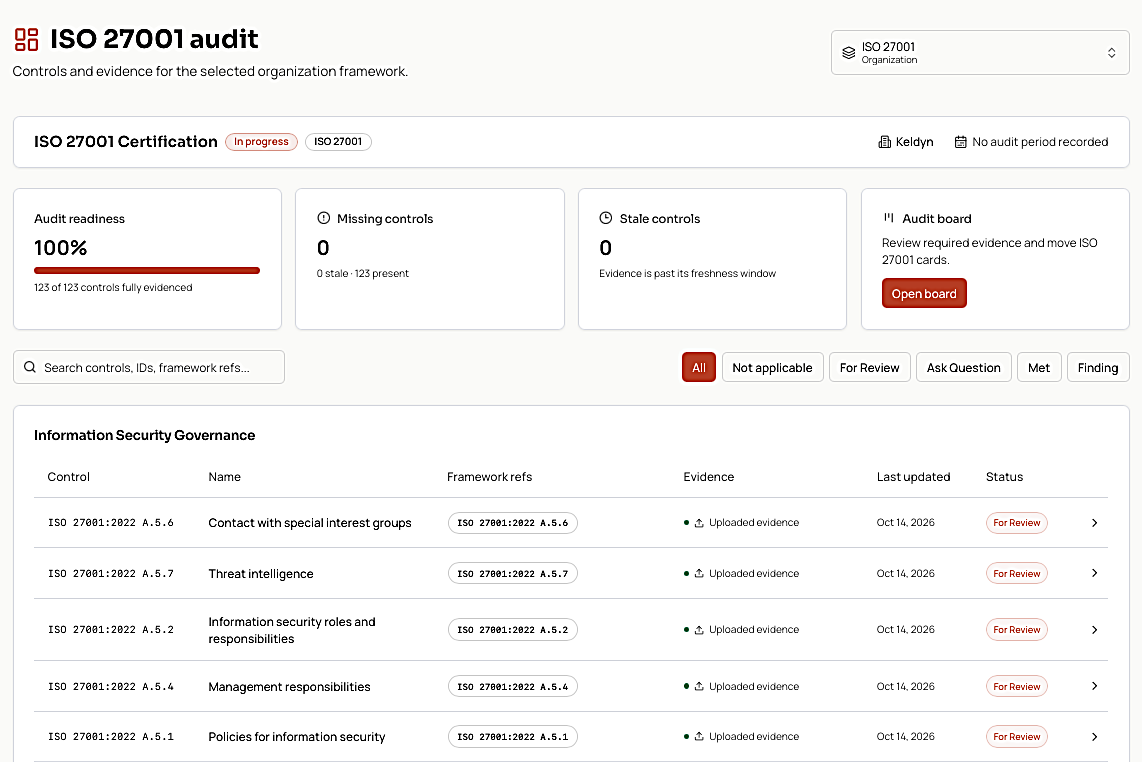
Evidence from your tools and your checks, ready for your auditor. Review the scope, risks and evidence with your team.
Evidence and audit →Keldyn helps you prepare. An accredited certification body makes the certification decision.
Frequently asked questions
What is ISO 27001 certification?
It is certification of an information security management system against ISO/IEC 27001, within a defined scope. An accredited certification body assesses the system and makes the certification decision.
Should we use ISO 27001:2013 or ISO 27001:2022?
Use ISO/IEC 27001:2022. The transition period from the 2013 edition has ended.
What happens at Stage 1 and Stage 2?
Stage 1 reviews documentation, scope and readiness. Stage 2 assesses implementation and effectiveness using evidence of how your management system and controls operate.
What happens after ISO 27001 certification?
The three-year certification cycle includes surveillance audits and recertification. Continue internal audits, management reviews, risk assessment and corrective actions between audits.
Does ISO 27001 cover AI governance?
It covers information security management. ISO 42001 adds AI management requirements, so teams adding AI governance should consider the standards together.
“You should be building to compliance rather than fixing to it.”
 Tim Brown
Co-Founder, Kyance