SOC 2 compliance and Type 2 for AI teams

    SOC 2 compliance means putting the relevant controls into practice. Prepare for a SOC 2 Type 2 report with requirements for your agents, checks before merge and evidence ready for your auditor.

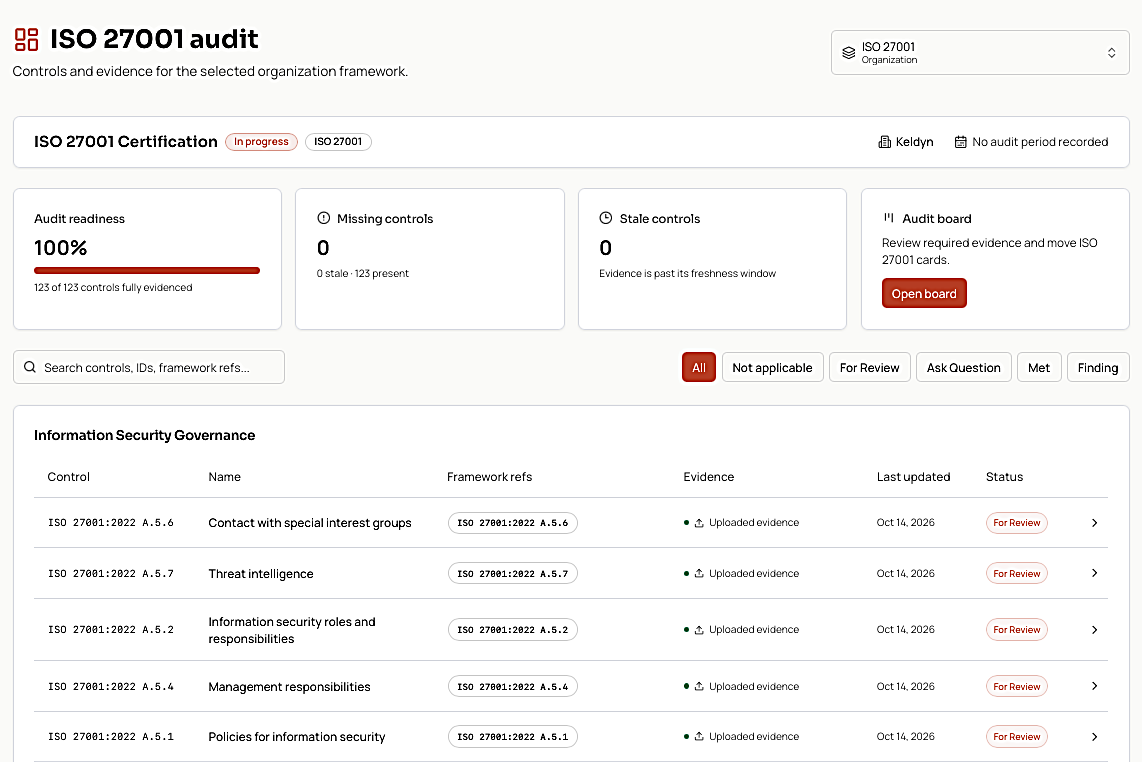
    Keldyn auditor portal showing audit readiness and control evidence
    At a glance
    What it is
    An AICPA attestation report on your controls against the Trust Services Criteria. It is a report, not a certification.
    Report types
    Type 1 covers control design at a point in time. Type 2 covers how controls operate over a period.
    Who issues it
    An independent CPA firm.
    Who asks for it
    Enterprise buyers asking for evidence of your security controls.
    Keldyn's role
    Prepares you for audit and introduces auditors.
    On this page

    Why AI startups get asked for SOC 2

    Enterprise buyers ask for evidence of your security controls. Security questionnaires bring those questions into the buying process. A SOC 2 report helps you show how your controls are designed and how they operate.

    SOC 2 Type 1 and Type 2 side by side

    1. Control design at a point in time
      Type 1

      Used when buyers want to see that your controls are designed appropriately on a given date. Issued by an independent CPA firm.

    2. Control operation over a period
      Type 2

      Used when buyers want evidence that controls operated over a defined period. Issued by an independent CPA firm.

    Ask your buyer which report they need.

    SOC 2 in brief

    • Type 1 covers control design at a point in time.
    • Type 2 covers how controls operate over a period.

    SOC 2 is an AICPA attestation report on your controls against the Trust Services Criteria. It is a report, not a certification.

    Is SOC 2 a certification?

    SOC 2 is not a certification. It is an attestation report issued by an independent CPA firm using the AICPA Trust Services Criteria. A SOC 2 Type 2 report examines how controls operated over a defined period, rather than certifying the company.

    Why it is harder when you ship with AI coding agents

    Code volume grows and changes move fast. Evidence can fall behind the work. Your security and compliance requirements need to be part of the engineering workflow, rather than reconstructed afterwards.

    SOC 2, ISO 27001 and ISO 42001 compared

    TopicSOC 2ISO 27001ISO 42001
    What it isAttestation reportCertification of an information security management systemCertification of an AI management system
    Who issues itIndependent CPA firmAccredited certification bodyAccredited certification body
    What it coversControls against the Trust Services Criteria in your scopeYour ISMS and Annex A controls, within the certified scopeYour AI management system, including AI risk, impact assessment and the AI system life cycle
    ValidityThe report covers a period; buyers usually expect a recent report3-year certificate with annual surveillance audits3-year certificate with annual surveillance audits
    Common buyersUS-led buyers often ask for SOC 2UK and EU buyers often ask for ISO 27001Buyers with AI-specific governance questions

    How Keldyn helps

    01

    Give agents your requirements

    Keldyn MCP gives coding agents your SOC 2 requirements before they build.

    Secure design →
    02

    Check before merge

    The compliance gate checks every change against your requirements before it merges.

    Compliance gate →
    03

    Get your policies in place

    Policies drafted from proven templates and the facts you confirm.

    Documents →
    04

    Evidence ready for your auditor

    Evidence from your tools and your checks, ready for your auditor. Your Trust Centre shares your security work with buyers.

    Evidence and audit →

    Qualified auditors and security specialists are your customer success team. Keldyn prepares you for audit and introduces auditors.

    Explore Trust Centre →

    The Kyance story

    SOC 2 controls built into Kyance’s agentic commerce platform.

    SOC 2, built in rather than bolted on.

    You should be building to compliance rather than fixing to it. Having it run inside the workflow while you build is, to me, immeasurable.
    Tim Brown
    Tim Brown, Co-Founder, Kyance
    Requirements mapped while the architecture was still moving
    Findings pushed straight into Jira as tickets
    Refactor checked in minutes: nothing regressed
    Read the story →

    Frequently asked questions

    What does SOC 2 compliance mean?

    It means implementing and operating controls relevant to the Trust Services Criteria in your scope. An independent CPA firm assesses those controls and issues a report.

    What is a SOC 2 Type 2 report?

    A SOC 2 Type 2 report covers how controls operate over a defined period. Type 1 covers their design at a point in time. Ask your buyer which report they need.

    Does Keldyn do the audit?

    No. An independent CPA firm issues the report. Keldyn prepares you and introduces auditors.

    Can we do ISO 27001 too?

    Yes. Controls overlap, and Keldyn covers both SOC 2 and ISO 27001.

    “You should be building to compliance rather than fixing to it.”
    Tim BrownTim Brown
    Co-Founder, Kyance
    Read the Kyance story →
    Trusted by teams at
    BoardlyKyanceVerinityHybrid AIMX3
    Qualified lead auditors on our team

    See how Keldyn fits your team.