SOC 2, built in rather than bolted on.
You should be building to compliance rather than fixing to it. Having it run inside the workflow while you build is, to me, immeasurable.
api/routes/account.ts:42services/auth/login.ts:118You want a large ecosystem with 400+ integrations and 35+ frameworks.
You want to choose from a partner network of 100+ audit firms, with Trust Center, vendor risk and questionnaire automation in one place.
You want qualified auditors and security specialists on your team doing the heavy lifting with you.
You want evidence collected from the work your engineers already do, with an independent auditor issuing the report.
You want AI assistants to read compliance data through a hosted MCP server (beta) in Claude Code, Cursor or Perplexity.
You want an official Claude Code plugin that fixes failing tests by generating infrastructure-as-code changes and opening a pull request.
You want your coding agents to get your security and compliance requirements before they build.
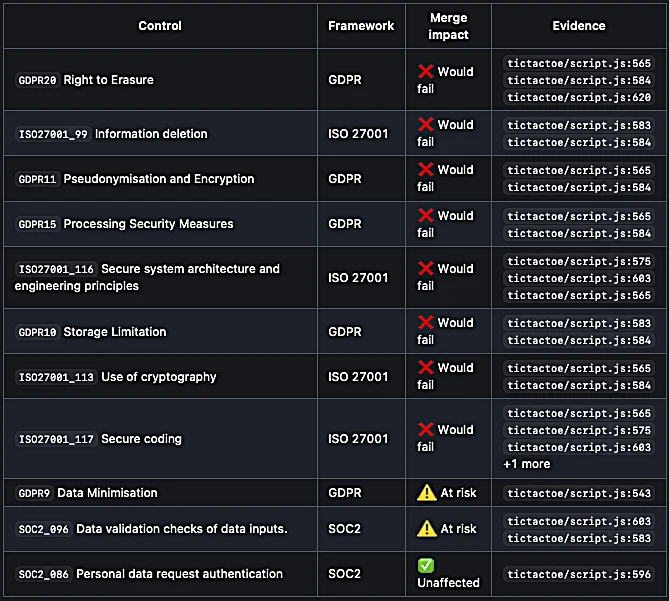
You want every application-code change checked against your own controls at the pull request, and turned into audit evidence.
As documented on Vanta's public site, reviewed 13 November 2026
| What matters | Vanta | Keldyn |
|---|---|---|
| Built for | Security and GRC teams. | Engineering-led teams shipping with AI. |
| Coding agents | MCP server and Claude Code plugin to read compliance data and fix failing tests. | Requirements given to the agent before it builds. |
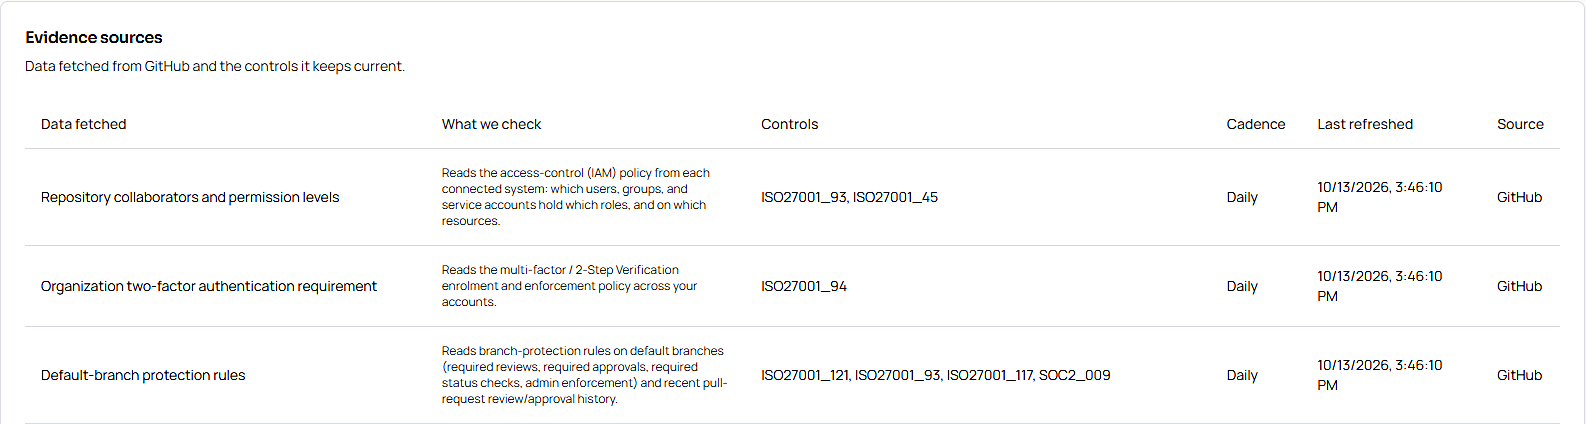
| Pull requests | Repository settings and pull request metadata such as approvals and automated checks. Vanta's GitHub integration guide says Vanta never reads the contents of your code. A pull request status check is not documented. | Every change checked against your controls before merge. |
| Audit | Partner network of 100+ audit firms. | Qualified auditors on your team; an independent auditor issues the report. |
| Trust Center | Yes. | Yes. |
| Frameworks | 35+ frameworks. | SOC 2, ISO 27001, ISO 42001, EU AI Act, GDPR, DORA, NIS2, OWASP, MITRE |

"The first time I ran it, it went through the whole codebase, told me what was missing, and pushed the lot into Jira as tickets. It did a serious amount of my work for me."
Tim Brown, Co-Founder, KyanceMapped while the architecture was still moving.
Findings surface in the coding agent and land in Jira.
Fixes and configuration build up against the audit from the start.
Every major platform now connects to AI assistants. The difference is what happens to the code: Keldyn checks your application code against your own controls, both before the agent builds and at the pull request, and turns that into audit evidence.
Keldyn MCP gives coding agents your security and compliance requirements while they build.
Explore Secure design →
The compliance gate checks every change against your rules before it merges.
Explore Compliance gate →
Evidence from your tools and your checks, ready for your auditor. Share your security work with buyers through your Trust Centre.
Explore Evidence and audit →Keldyn can sit in the engineering workflow while you keep your existing GRC programme. Your team can move its compliance programme across when ready, at a pace that works for you.
SOC 2 reports come from an independent CPA. ISO certificates come from an accredited body. We introduce you, and we're in the room.

Yes, for engineering-led teams that want security and compliance in their development workflow. Keldyn gives coding agents your requirements before they build and checks every change before merge.
Certifications and reports: SOC 2, ISO 27001 and ISO 42001. Compliance with EU AI Act, GDPR, DORA and NIS2. Application security against OWASP and MITRE.
No. You can keep Vanta while Keldyn sits in your engineering workflow, and move your compliance programme across when you're ready.
Qualified auditors and security specialists are your customer success team. They work with you on security and compliance alongside your engineering team.
Last reviewed 13 November 2026. Comparison based on each company's public documentation. Product names are trademarks of their owners.